Access control
Firm users and client portal users operate through distinct access patterns and permissions.
Fairness is designed around separate firm workspaces, controlled client access, dedicated authentication surfaces and auditable legal workflows.
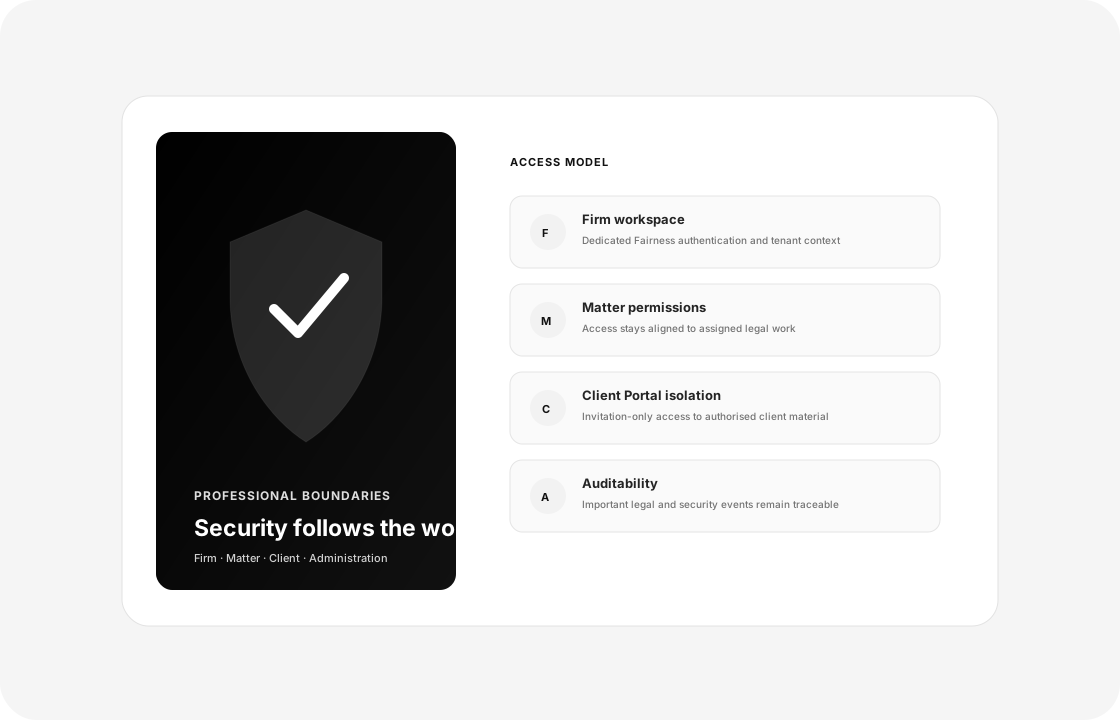
Fairness separates the firm workspace, matter access, client portal and administrative functions so the security model reflects the way professional legal work is actually organised.
Fairness security is designed as part of the product boundary, not as a marketing layer added afterwards.
Firm users and client portal users operate through distinct access patterns and permissions.
Fairness workspace, client portal and platform administration use dedicated Fairness authentication boundaries.
Sensitive authentication flows can use MFA and request throttling to reduce account abuse.
Important legal, security and administrative actions are designed to remain traceable.
Matter documents support controlled access, review states, versions and integrity-oriented metadata.
Fairy is permission-aware and remains subject to professional review and configured provider boundaries.
Bring matters, case files, client collaboration, billing and Fairy into one professional environment.